ITAD
IT Asset Disposition Services, On-Site Worldwide
Reboot Monkey coordinates the full ITAD lifecycle at your datacenter facility. Secure data destruction to NIST 800-88 standards, hardware remarketing, recycling through partner facilities, and complete chain of custody documentation. Available across 190 countries and more than 400 locations.
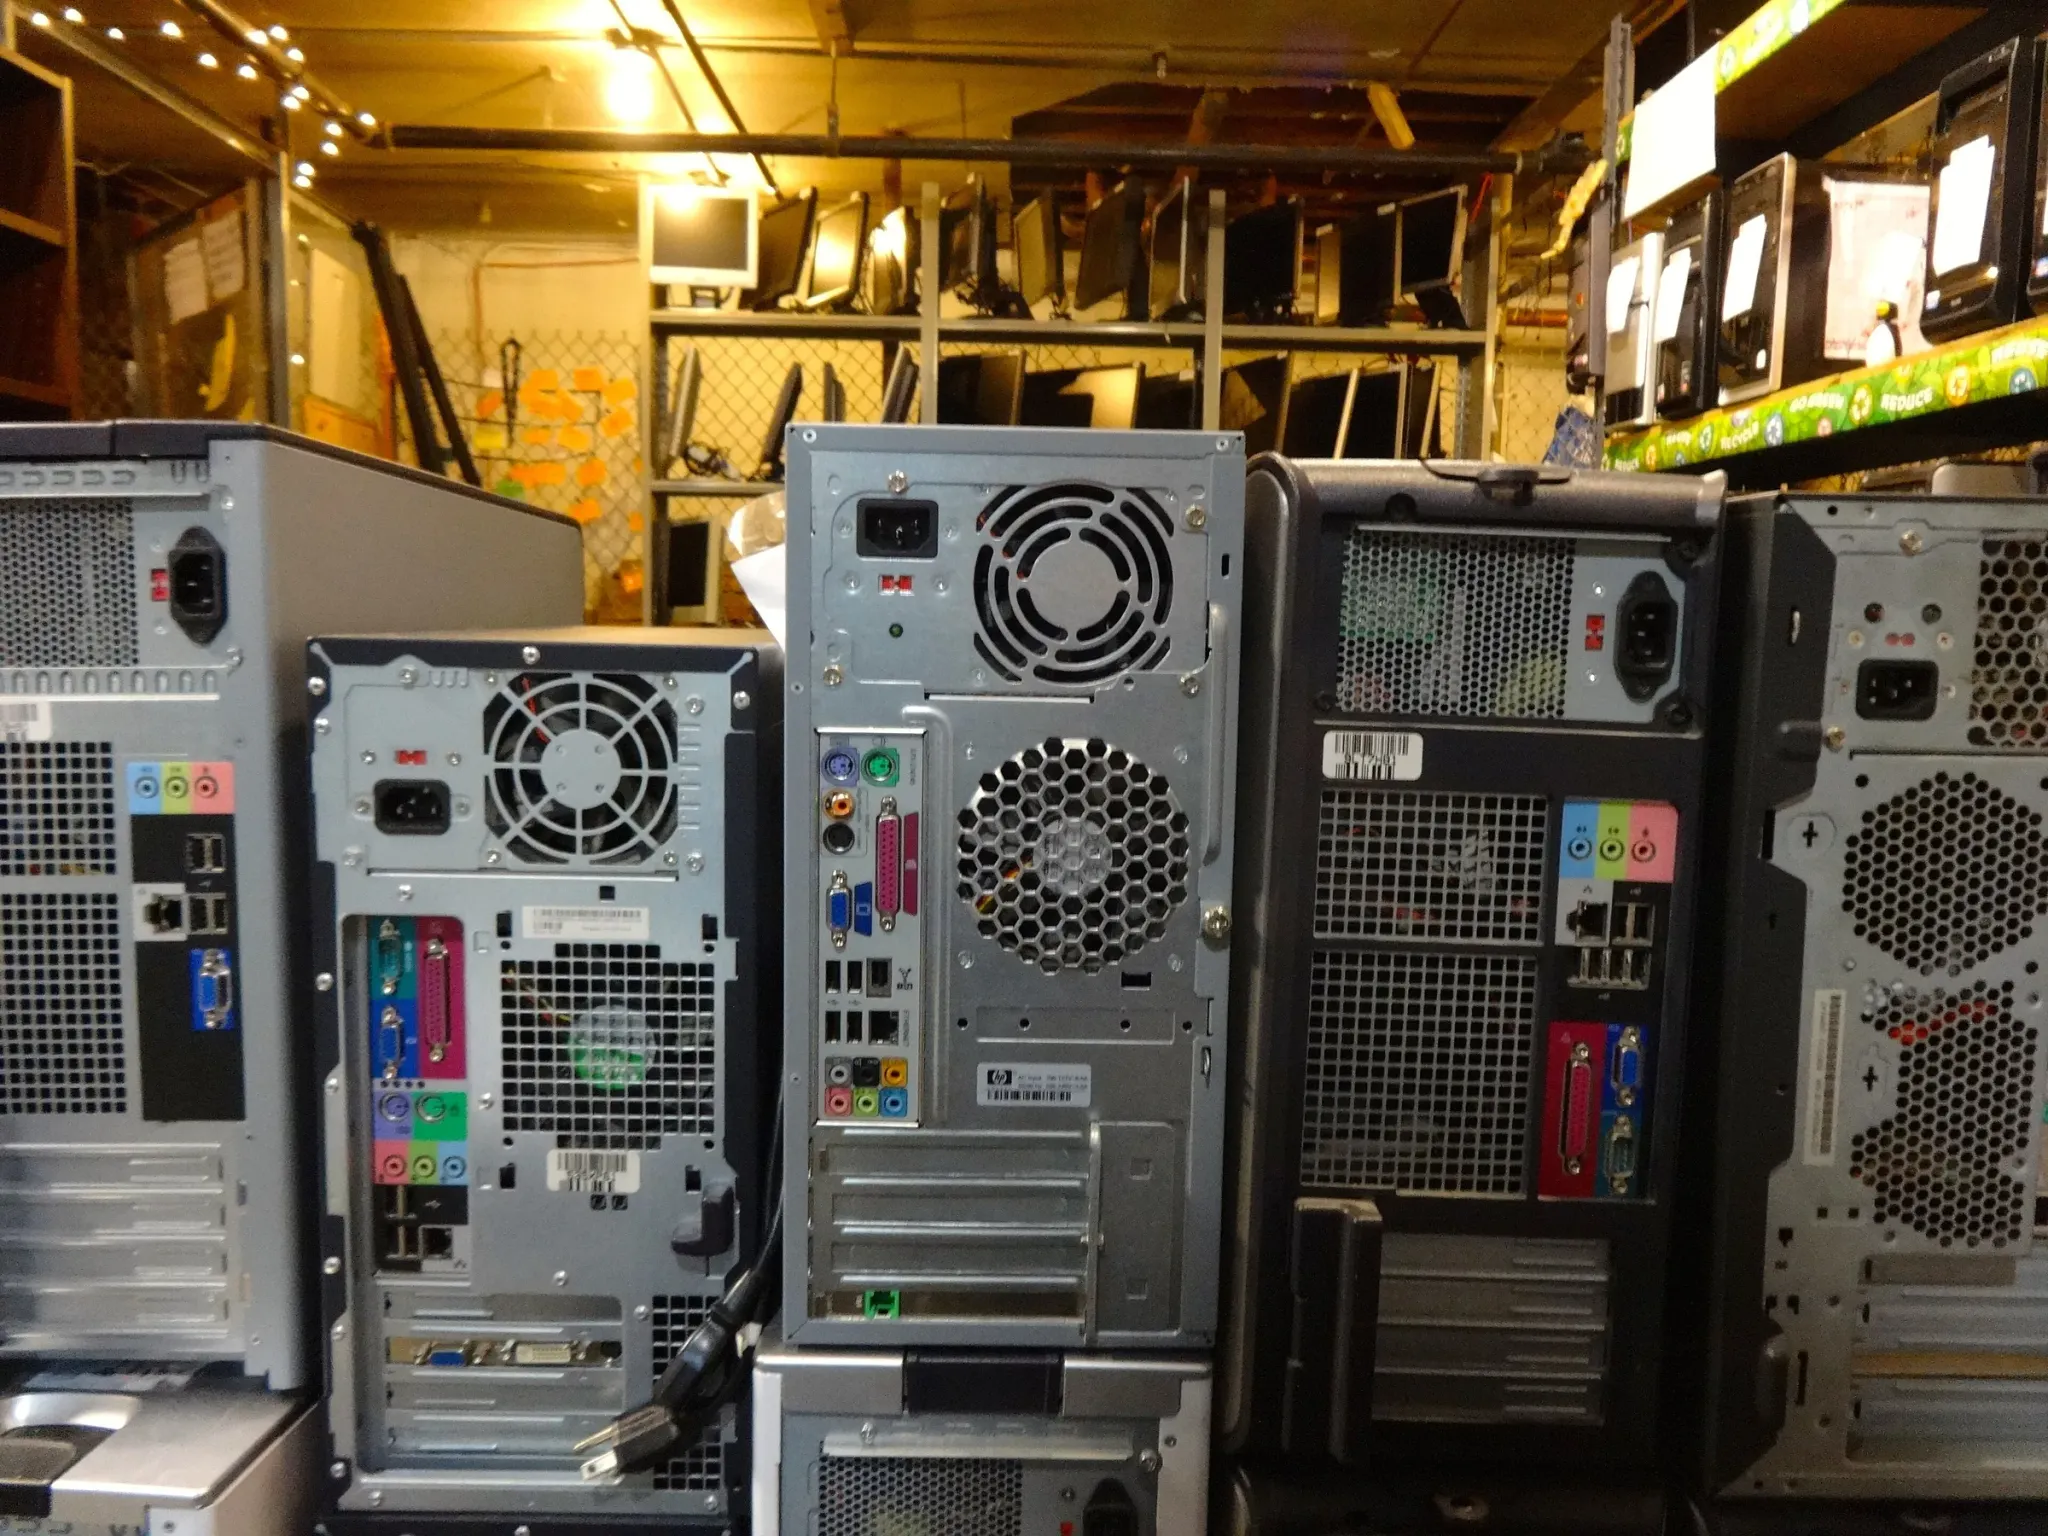
ITAD
- 1
- agreement for every city
Related Services
On-Site Hardware Audit and Inventory
Physical asset inventory at your datacenter facility. Serial number logging, hardware configuration capture, condition assessment, and remarketability triage. Foundation of chain of custody documentation.
NIST 800-88 Data Destruction
Secure data destruction per NIST SP 800-88 Rev 1. Method selection (Clear, Purge, or Destroy) based on your data classification and compliance requirements. Per-device destruction certificates issued.
Hardware Remarketing and Value Recovery
Resale and refurbishment coordination for equipment with residual market value. Vendor-neutral assessment across Dell, HP/HPE, Cisco, Juniper, Arista, Supermicro, and Lenovo. Value recovery accounting in final documentation.
Recycling Coordination
Routing of non-remarketable equipment through partner facilities, with a certificate of destruction per storage device and chain of custody documentation.
Logistics and Cross-Border Coordination
Asset transport from your facility to downstream partners. Transport manifests, chain of custody continuity, and Basel Convention compliance for international projects.
Chain of Custody Documentation
Complete per-device audit trail from on-site inventory through final disposition. Destruction certificates and transport manifests consolidated into an audit-ready package.
Data Center ITAD
Full ITAD lifecycle coordination at third-party colocation facilities. On-site execution within facility access and escort protocols. Covers Equinix, Digital Realty, and regional colo operators globally.
Data Center Decommissioning Integration
ITAD coordinated as part of a full datacenter decommissioning project. Asset disposition sequenced with power-down, disconnection, and facility handback. Single point of coordination for the full scope.
How we run every job
Plan
You tell us the building, the rack and the job; we agree scope and timing.
Access
You add our engineer to the building's access list as your visitor.
On site
An engineer does the work in your rack, on your instruction.
Sign-off
You confirm the work; it is billed under your one agreement.
The building's own staff vs Reboot Monkey
| The building's own staff | Reboot Monkey | |
|---|---|---|
| Works for | The building | You |
| Other operators' buildings | No | Yes |
| Several cities | One agreement per operator | One agreement for all |
In depth
ITAD: 9 sections, open any to read more.
What Is ITAD (and Why It Is Not Just Recycling)
IT Asset Disposition (ITAD) is the structured, compliant process for retiring end-of-life IT hardware. The term covers everything from the initial on-site audit through secure data destruction, hardware remarketing, recycling, and final compliance documentation. Disposition is deliberate. Recycling alone is not ITAD.
When enterprises confuse ITAD with generic recycling, they skip the two steps that matter most for risk management: verified data destruction and documented chain of custody. A server handed to a recycler with no destruction certificate is a compliance liability, not a decommissioned asset. For organizations subject to GDPR, HIPAA, SOX, or ISO 27001:2022, that liability is real and auditable.
Reboot Monkey is a 3rd-party datacenter services provider. We are not a recycling facility. We coordinate the full ITAD lifecycle on-site at your facility, then route assets through downstream partners for remarketing or material recovery. The distinction matters: our technicians arrive at your equipment room, not a warehouse loading dock.
- ITAD = IT Asset Disposition (not disposal). Encompasses data destruction, remarketing, recycling, and compliance documentation
- Generic recycling skips data destruction and chain of custody, creating regulatory risk
- On-site ITAD at your datacenter reduces data exposure during transit
- ISO 27001:2022 Annex A Control 7.14 explicitly requires secure disposal of data and equipment
The ITAD Lifecycle: Six Phases from Audit to Certificate
Reboot Monkey manages each phase of ITAD as a coordinated sequence, not a single handoff to a third-party recycler. Every phase generates documentation that feeds the final chain of custody record.
Phase 1, Pre-Audit Assessment, begins on-site. Our technicians perform a physical inventory of all assets scheduled for disposition, logging serial numbers, model numbers, hardware configurations, and condition ratings. This baseline inventory is the foundation of chain of custody. No asset moves without an audit entry.
Phase 2, Data Destruction, follows NIST SP 800-88 Rev 1 guidelines. Three methods apply depending on data sensitivity and hardware reuse intent: Clear (logical overwrite for hardware entering secondary markets), Purge (physical or cryptographic erasure for sensitive data), and Destroy (physical destruction of media for maximum assurance). We apply the method your compliance framework requires. Destruction certificates are issued per device.
Phase 3, Hardware Triage and Remarketing, recovers value from functional or refurbishable equipment. Working servers, networking gear, and storage arrays enter the secondary market through our partner network. Hardware 2 to 3 years old typically recovers 40 to 60 percent of original value. Older commodity hardware recovers 10 to 20 percent. That recovery offsets or eliminates disposition costs in many projects.
Phase 4, Recycling, handles assets with no residual market value. We route this material through partner facilities, where it is processed by Reboot Monkey staff.
Phase 5, Logistics Coordination, manages physical asset movement from your facility to partner sites. We handle transport documentation, cross-border compliance where applicable, and chain of custody continuity at every handoff point. The Basel Convention governs transboundary e-waste movement for international projects, and our logistics protocols account for those requirements.
Phase 6, Compliance Documentation, closes the project. You receive a final chain of custody report, per-device data destruction certificates, and an audit-ready asset disposition record. This package satisfies GDPR, SOX, HIPAA, and ISO 27001 audit requirements.
- Phase 1: On-site hardware audit and serial-number inventory
- Phase 2: NIST 800-88 data destruction (Clear / Purge / Destroy as required)
- Phase 3: Hardware remarketing, value recovery of 10-60% of original asset value
- Phase 4: Recycling through partner facilities
- Phase 5: Logistics coordination and cross-border Basel Convention compliance
- Phase 6: Chain of custody documentation, destruction certificates, audit package
On-Site ITAD at Third-Party Colocation Facilities
This is the ITAD use case that tier-1 providers do not address. Iron Mountain, Sims Lifecycle Services, and ERI are logistics-first operations. They collect equipment, process it at their facilities, and return documentation. That model works for office hardware. It does not work when your infrastructure lives in an Equinix cage in Frankfurt or a Digital Realty suite in Singapore.
At a third-party colocation facility, you own the equipment but you do not control the building. Decommissioning requires coordination with the facility operator, adherence to the facility's access and escort policies, and physical removal that does not disrupt adjacent tenants. A standard ITAD pickup request does not cover that.
Reboot Monkey dispatches field technicians directly to the colocation facility. We work within the facility's escort and access rules. Our technicians handle equipment removal, tag and inventory each asset on-site, execute data destruction at the rack before any hardware leaves the floor, and coordinate removal logistics with facility operations. No competitor has built content around this workflow, let alone a service model for it, because it requires operational infrastructure in the facility's city, not just a pickup truck and a loading dock.
This matters for a specific buyer: the enterprise or cloud-native company with infrastructure distributed across 10 to 50 colocation locations globally. Each facility has its own access protocols, its own power and cooling constraints for decommissioning sequencing, and its own documentation requirements. Coordinating ITAD across that footprint from a single centralized provider is a coordination problem, not a logistics problem. Reboot Monkey is structured to solve that problem because we operate in 190 countries and more than 400 locations.
- Colocation ITAD requires compliance with facility access, escort, and removal policies
- On-site data destruction at the rack before hardware leaves the floor
- No competitor addresses the on-site colocation ITAD use case in their content or service model
- Reboot Monkey operates in 190 countries and more than 400 locations: the same footprint as your colocation estate
- Multi-facility ITAD coordination across Equinix, Digital Realty, and regional colo operators
Data Destruction Standards and Compliance Frameworks
Data destruction compliance is not a single standard. The framework that governs your ITAD project depends on your industry, the data classification of the equipment being retired, and the jurisdictions where that equipment was operated.
NIST SP 800-88 Rev 1 is the U.S. federal standard for media sanitization and the reference framework most enterprise ITAD contracts specify. It defines three methods: Clear, which uses logical overwriting and is appropriate for hardware entering secondary markets; Purge, which employs physical or cryptographic techniques to prevent laboratory-grade data recovery; and Destroy, which renders media physically non-functional for maximum assurance. The method selection is driven by data sensitivity classification, not by default. Reboot Monkey applies the method your security policy requires.
For organizations in regulated industries, additional frameworks apply. HIPAA requires covered entities to implement policies for the final disposition of electronic protected health information and hardware on which it resides. SOX requires financial-sector organizations to maintain audit trails for records management and data disposition. GDPR Article 17 creates the right to erasure, which for hardware disposition means verifiable, documented data destruction with certificates that can be produced on audit.
ISO 27001:2022 addresses equipment disposal directly in Annex A Control 7.14, requiring that all equipment containing storage media be verified before disposal or reuse. For organizations pursuing or maintaining ISO 27001 certification, a compliant ITAD process is not optional.
Our ITAD partner's sites include facilities certified to ISO 9001, ISO 14001, ISO/IEC 27001 and ISO 45001. Ask us for the certificate of the site that handles your job.
- NIST 800-88 Rev 1: Clear (logical overwrite), Purge (cryptographic/physical), Destroy (physical destruction)
- HIPAA: Requires documented disposal procedures for all ePHI-bearing hardware
- SOX: Audit trail requirements for data disposition in financial-sector organizations
- GDPR Article 17: Right to erasure requires destruction certificates producible on audit
- ISO 27001:2022 Annex A Control 7.14: Equipment disposal is a mandatory security control
- Certificate of the partner site that handles your job available on request
Hardware Remarketing and Value Recovery
ITAD is not purely a cost center. Done correctly, hardware remarketing converts end-of-life equipment into recoverable budget. The economics depend on equipment age and market demand, but the principle holds across most datacenter refresh cycles.
Modern servers decommissioned at 2 to 3 years into a lifecycle typically recover 40 to 60 percent of original purchase value through enterprise secondary markets. Older commodity hardware, at 5 to 7 years, recovers 10 to 20 percent. Specific components, including high-density memory, NVMe storage, and recent-generation Cisco and Juniper networking gear, often command stronger recovery rates because enterprise secondary buyers compete for them.
Reboot Monkey assesses remarketability during the Phase 1 audit. Assets flagged as remarketable are inventoried, processed for data destruction as required (Clear or Purge), and routed to our partner network for resale or refurbishment. Assets with no residual market value go directly to recycling partners. You receive value recovery accounting as part of the final documentation package.
The vendor-neutral aspect of Reboot Monkey's model matters here. We are not affiliated with any OEM and have no incentive to route specific hardware to specific secondary channels. Our technicians are certified across Dell, HP/HPE, Cisco, Juniper, Arista, Supermicro, and Lenovo. That breadth means we assess the full equipment mix accurately rather than defaulting to OEM-preferred disposition channels that may not optimize your recovery.
- 2-3 year-old servers typically recover 40-60% of original asset value
- Older commodity hardware recovers 10-20% through secondary markets
- High-density memory, NVMe storage, and recent Cisco/Juniper gear command premium recovery rates
- Vendor-neutral assessment across Dell, HP/HPE, Cisco, Juniper, Arista, Supermicro, Lenovo
- Value recovery accounting included in final ITAD documentation package
Chain of Custody: The Legal Foundation of Compliant ITAD
Chain of custody is not a feature. It is the legal and contractual proof that your hardware was handled, destroyed, and disposed of in a compliant manner from the moment it left your equipment room to its final destination. Without it, you cannot respond to a regulatory audit, a data breach investigation, or a client contract requirement for disposal certification.
Reboot Monkey's chain of custody documentation captures every handoff. The pre-audit inventory logs each asset by serial number, model, and location. Data destruction generates per-device certificates with method, technician ID, date, and applicable standard. Physical asset movement from your facility to our partners generates transport manifests.
The complete package is the deliverable. Not a single form confirming collection. A complete, per-device audit trail covering every phase from on-site audit through final disposition, in a format that satisfies SOC 2 Type II auditors, HIPAA covered entity compliance reviewers, and GDPR data protection officers.
For multi-facility projects, we consolidate chain of custody documentation across all sites into a single audit package. Enterprise IT directors managing infrastructure across 20 colocation locations should not receive 20 separate unformatted PDF bundles. They receive one organized record set they can file and reproduce on demand.
- Per-device data destruction certificates with method, standard, technician ID, and date
- Transport manifests documenting asset movement at every handoff
- A certificate of destruction per storage device
- Consolidated audit package for multi-facility projects
- Documentation format satisfies SOC 2, HIPAA, GDPR, and SOX audit requirements
Global ITAD Coverage: 190 countries and more than 400 locations
Most ITAD providers are operationally concentrated in North America and Western Europe. When your infrastructure extends beyond those markets, you encounter the same provider but with fewer guarantees about on-site capability, response time, and regulatory knowledge at the local level.
Reboot Monkey operates field technicians in 190 countries and more than 400 locations. Our 24/7 NOC supports a 1-hour response SLA, with on-site response times agreed per site. That coverage includes the primary colocation markets (Frankfurt, London, Amsterdam, Paris, New York, Los Angeles, Dallas, Chicago, Singapore, Tokyo, Sydney, Dubai, Johannesburg) and secondary markets that enterprises expand into but traditional ITAD providers thin out on.
Global ITAD projects introduce regulatory complexity that a single-jurisdiction provider cannot navigate. The Basel Convention governs the transboundary movement of hazardous e-waste across 190+ signatory nations. The EU WEEE Directive (2012/19/EU) mandates specific recovery and recycling rates for IT equipment across EU and EEA markets, with collection and documentation requirements that differ from North American practices. Extended Producer Responsibility (EPR) frameworks in the EU, Canada, and several Asia-Pacific jurisdictions assign compliance obligations that vary by country and equipment category.
We operate in these jurisdictions, not around them. Local field presence means local regulatory awareness, local partner relationships, and local documentation that satisfies in-country compliance requirements.
- Field technician coverage in 190 countries and more than 400 locations
- 24/7 NOC support with 1-hour response SLA and on-site times agreed per site
- Basel Convention compliance for transboundary e-waste movement
- EU WEEE Directive (2012/19/EU) compliance for EU/EEA projects
- Local recycling partners in key markets
- Coverage across FLAP-D, Nordics, US hubs, APAC, Middle East, and Africa
Why Enterprises Choose Reboot Monkey Over Tier-1 ITAD Providers
Iron Mountain is the category leader in ITAD. Their operation is built around centralized processing at proprietary facilities, integrated with their records management and physical storage business. If your decommissioning project involves shipping hardware to a facility and receiving documentation back, Iron Mountain has the scale for that. Where they do not perform is on-site at a third-party colocation facility, where their centralized model creates a logistics handoff that interrupts chain of custody and requires facility coordination they are not positioned to execute.
Sims Lifecycle Services leads in circular economy messaging and ITAD program governance tools. Their 40-page ITAD program guide and vendor selection frameworks are genuinely useful for procurement teams. But Sims, like Iron Mountain, is a centralized processing model. No content, no service description, and no case study on their site addresses the colocation on-site ITAD scenario.
ERI holds SOC 2 Type II certification and operates the largest fully integrated ITAD and hardware destruction capacity in North America. For Fortune 500 organizations running hyperscale infrastructure in the US, ERI is a credible option. For distributed global infrastructure outside North America, ERI's geographic reach is limited.
Reboot Monkey is not a recycling facility. We are a 3rd-party datacenter services operator. Our field technicians have been inside Equinix, Digital Realty, and hundreds of regional colocation facilities. We know what it takes to decommission equipment in a live, multi-tenant environment without disrupting adjacent tenants, violating facility rules, or creating a chain-of-custody gap. That is a different capability than running a recycling facility, and it is the capability that matters when your hardware sits in a colo cage 6,000 miles from your headquarters.
- Iron Mountain: centralized processing model, not positioned for on-site colocation ITAD
- Sims: strong governance tools, but no on-site colocation service capability
- ERI: North America-centric, limited global coverage outside US
- Reboot Monkey: on-site at your colocation facility, globally, with full chain of custody
- Vendor-neutral technicians certified across Dell, HP/HPE, Cisco, Juniper, Arista, Supermicro, Lenovo
- Integrated with Reboot Monkey remote hands, rack-and-stack, and datacenter migration services
ITAD Engagement Models and Pricing
Reboot Monkey offers three engagement structures for ITAD projects, designed to fit the operational and financial model of each client.
Per-incident engagements apply to unplanned or one-time disposition needs: an emergency decommissioning, a lease termination requiring rapid asset clearance, or an M&A-driven consolidation with a fixed deadline. Pricing is scoped per project based on asset count, facility access complexity, data destruction requirements, and logistics.
Block-hours engagements suit planned ITAD projects with predictable resource requirements. A scheduled datacenter refresh across two colocation sites, for example, is better served by pre-purchased hours that provide cost certainty and guaranteed resource availability without repeated per-incident pricing.
Retainer engagements serve enterprises managing continuous hardware lifecycle programs across multiple facilities. A global financial services firm retiring hardware on a rolling 3-year refresh cycle across 15 colocation locations does not want to re-scope each project individually. A retainer provides ongoing ITAD coordination as a managed service, with standardized documentation, consolidated reporting, and a dedicated point of contact.
Pricing variables for all engagement types include asset volume, geographic scope, destruction method required, facility access complexity, and whether remarketing value recovery is included. Contact us for a project-specific quote.
- Per-incident: one-time or emergency ITAD projects, scoped by asset count and complexity
- Block-hours: planned refresh cycles with cost certainty and guaranteed resources
- Retainer: ongoing ITAD coordination for multi-facility enterprise programs
- Value recovery from hardware remarketing offsets or eliminates disposition costs in many cases
- Pricing factors: asset volume, geography, destruction method, facility access
Frequently Asked Questions
What does ITAD stand for?
ITAD stands for IT Asset Disposition. It is the structured, compliant process for retiring end-of-life IT hardware, covering secure data destruction, hardware remarketing, recycling, and chain of custody documentation. ITAD is not synonymous with recycling. Recycling is one outcome within an ITAD program.
What is the difference between ITAD and IT recycling?
IT recycling addresses the physical material recovery of electronic hardware after end of life. ITAD encompasses that recycling step but also includes verified data destruction, hardware remarketing for value recovery, chain of custody documentation, and regulatory compliance reporting. For regulated organizations, recycling without the data destruction and documentation steps creates compliance liability.
What is NIST 800-88 and how does it apply to ITAD?
NIST SP 800-88 Rev 1 is the U.S. federal standard for media sanitization. It defines three destruction methods: Clear (logical overwrite for hardware entering secondary markets), Purge (physical or cryptographic destruction for sensitive data), and Destroy (physical destruction of media for maximum assurance). NIST 800-88 is the most widely referenced data destruction standard in enterprise ITAD contracts.
Does Reboot Monkey hold certifications, and what about its ITAD partner?
Reboot Monkey itself holds no certificate. Our ITAD partner's sites include facilities certified to ISO 9001, ISO 14001, ISO/IEC 27001 and ISO 45001. Ask us for the certificate of the site that handles your job. The certificates belong to the partner's sites, not to Reboot Monkey, which is a field services coordinator and on-site ITAD operator, not a recycling facility. Every job includes a certificate of destruction per storage device.
Can Reboot Monkey perform ITAD at a colocation facility?
Yes. This is a core use case. Reboot Monkey dispatches field technicians directly to third-party colocation facilities, including Equinix, Digital Realty, and regional colo operators. We work within the facility's access, escort, and removal protocols. On-site data destruction is performed at the rack before any hardware leaves the floor, maintaining chain of custody from the point of decommissioning.
What compliance frameworks does ITAD documentation support?
Reboot Monkey's ITAD documentation is structured to satisfy GDPR Article 17 (right to erasure), HIPAA disposal requirements for electronic protected health information, SOX audit trail requirements, and ISO 27001:2022 Annex A Control 7.14 equipment disposal controls. The chain of custody package includes per-device destruction certificates and transport manifests.
What value recovery can I expect from hardware remarketing?
Recovery rates depend on equipment age, condition, and current secondary market demand. Servers decommissioned at 2 to 3 years into their lifecycle typically recover 40 to 60 percent of original purchase value. Hardware at 5 to 7 years recovers 10 to 20 percent. High-demand components such as recent-generation memory, NVMe storage, and Cisco or Juniper networking gear command higher recovery rates. Reboot Monkey provides value recovery accounting as part of the final disposition report.
What is chain of custody documentation in ITAD?
Chain of custody documentation is the per-device audit trail that records every handoff from your equipment room through final disposition. It includes the pre-audit inventory with serial numbers, per-device data destruction certificates and transport manifests. This documentation is the primary evidence in a regulatory audit or data breach investigation involving decommissioned equipment.
Does Reboot Monkey handle international ITAD projects?
Yes. Reboot Monkey operates in 190 countries and more than 400 locations. International projects introduce cross-border compliance obligations including the Basel Convention, which restricts transboundary movement of e-waste, and regional frameworks such as the EU WEEE Directive. Our logistics protocols account for these requirements, and our documentation packages include the records required for cross-border compliance.
What engagement models does Reboot Monkey offer for ITAD?
Three models: per-incident (one-time or emergency projects), block-hours (planned refresh cycles with predictable resource needs), and retainer (ongoing multi-facility programs). Contact us to scope your project.